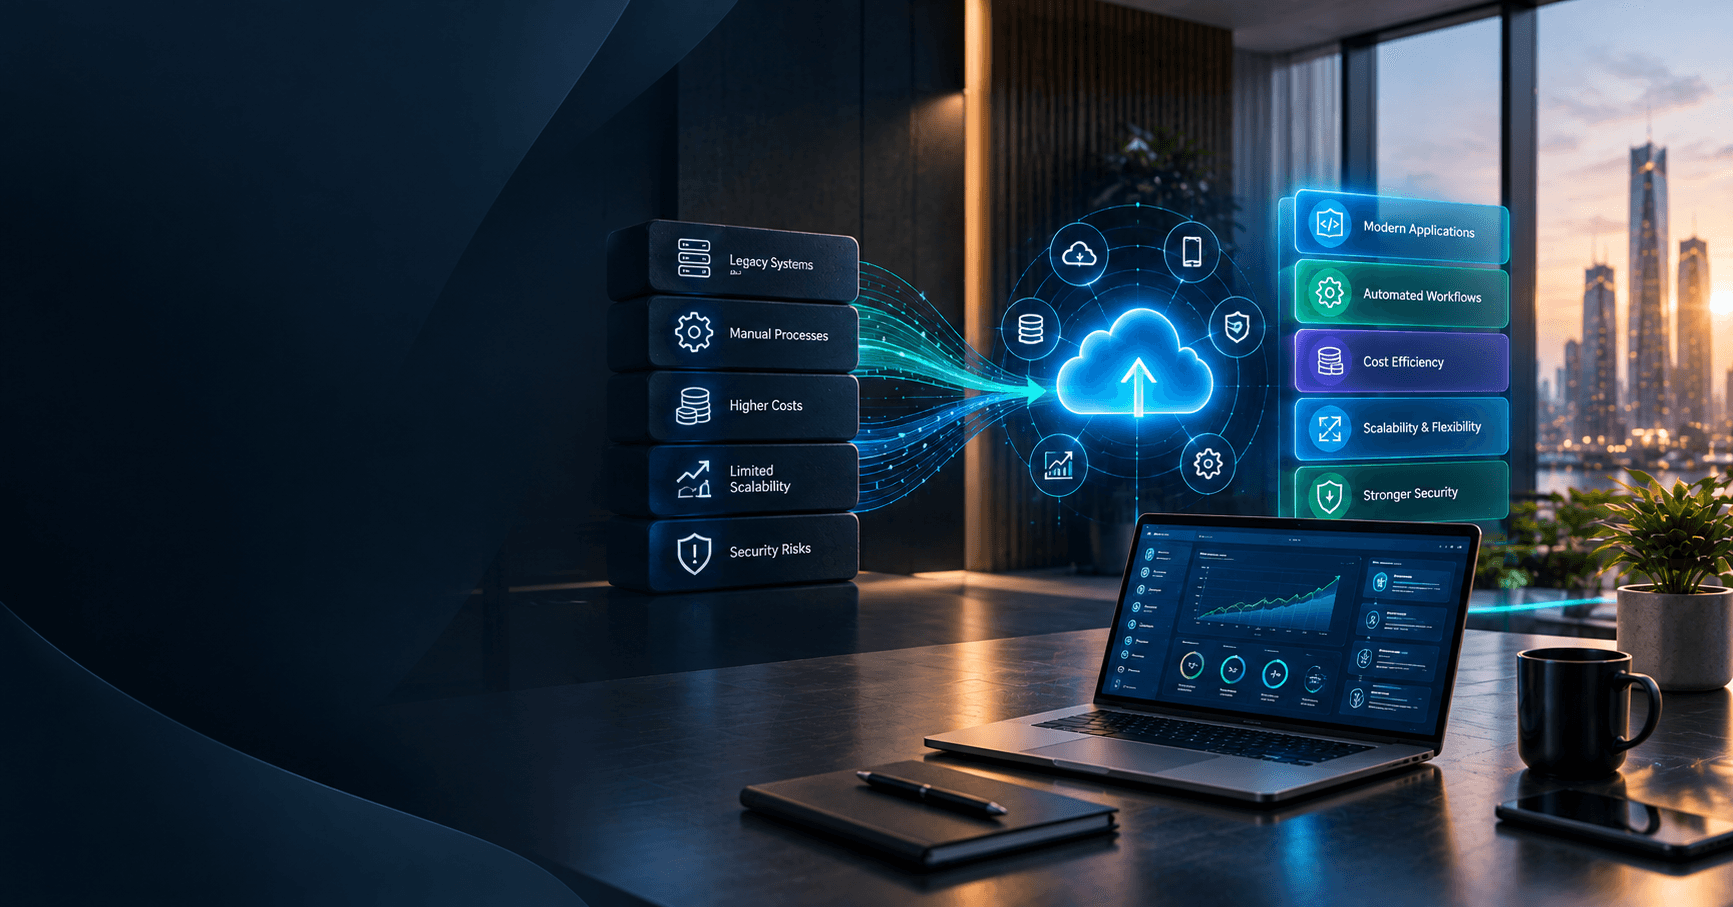
Enterprise modernization involves upgrading the systems, processes and operating model that hold a business back, so technology becomes easier to change, integrate, secure and scale. If you are asking what does enterprise modernization involve, and where do I start, start with a business-led assessment of your most critical applications, data flows, security risks and delivery bottlenecks, then prioritise changes that reduce risk or unlock value fastest.
Key takeaways
- Enterprise modernization usually involves updating legacy applications, data, infrastructure, security and delivery processes so technology can support faster change with less operational risk.
- The best place to start is not with a full rebuild, but with a clear assessment of business-critical systems, integration dependencies, security gaps and measurable outcomes.
- A phased modernization roadmap often combines quick wins, such as identity, observability or API layers, with longer-term work like replatforming, refactoring or replacing legacy applications.
- Security, data quality and change management should be designed into modernization from day one; adding them late is one of the most common reasons programmes stall.
- Typical modernization timelines range from a few months for a focused platform upgrade to 12 months or more for multi-system transformation across applications, data and operations.
What enterprise modernization actually means
For most established businesses, modernization is not a single project and it is not just moving systems to a new hosting environment. It usually spans legacy applications, databases, infrastructure, integration patterns, security controls, delivery workflows and user experience. The goal is practical: make core systems more reliable, secure, easier to extend and less expensive to operate over time.
In practice, that can mean different things depending on your starting point. A manufacturer might replace spreadsheet-driven planning with a web platform backed by APIs and role-based access. A professional services firm may modernise a monolithic client portal into modular services with single sign-on and audit trails. A retail or logistics business may keep its core ERP but introduce event-driven integrations, better reporting and resilient hosting so teams can release changes without weekend outages.
What counts as modern is also less about fashion than fit. A sensible target architecture may include:
- Cloud or hybrid hosting where elasticity, resilience or operational simplicity justify the move
- Containers or managed application platforms where deployment consistency matters and the team can support the added complexity
- Modern web or mobile stacks that are actively supportable and easier to hire for
- API-first integration using synchronous and asynchronous patterns where each suits the business process
- Managed data platforms where backup, patching and scaling are easier to govern
- Automated delivery pipelines with repeatable testing, releases and rollback
- Security controls such as single sign-on, multi-factor authentication, least-privilege access, encryption, secrets management and central logging
The key point is that enterprise modernization is a means to improve business agility and reduce operational drag. It is not an architecture trend exercise.
what does enterprise modernization involve, and where do i start?
The short answer is that modernization involves deciding what to retain, rehost, replatform, refactor, replace or retire across your applications, infrastructure and data. Where you start depends on business criticality: begin with the systems that create the most risk, delay or manual effort, then map dependencies before choosing any technology path.
A useful first step is a focused discovery phase. This does not need to become a six-month strategy programme. For many mid-sized organisations, two to six weeks is enough to document the current estate, identify pain points, interview operational stakeholders and produce a prioritised roadmap. Looking through four lenses together helps avoid rework later:
- Business: revenue impact, customer experience, compliance exposure, operational friction
- Technical: architecture debt, supportability, release process, integration complexity
- Data: ownership, quality, reporting gaps, migration difficulty, retention obligations
- Security and resilience: identity, access, patching, backup, recovery, monitoring, incident readiness
From there, classify each major system using a simple decision framework:
- Retain: the system works, is supportable and does not block change
- Rehost: move it largely as-is for operational reasons such as resilience or data centre exit
- Replatform: keep the application but improve runtime, database, hosting or deployment model
- Refactor: change code structure or service boundaries to improve maintainability, performance or scale
- Replace: adopt a more suitable platform or rebuild because the current solution is no longer fit
- Retire: remove unused or duplicated systems to reduce cost and risk
This framing helps leaders avoid a common mistake: assuming every older system needs a ground-up rebuild. Often, the highest-return early move is simpler, such as adding an API layer around a stable core, centralising authentication or introducing observability before deeper change begins.
Assess your current estate before choosing tools
Modernization programmes fail when businesses buy technology before understanding constraints. An honest baseline matters more than a polished future-state diagram. Inventory the applications in use, who depends on them, where the data lives, how integrations work, how releases happen, what fails most often and what nobody dares touch.
This assessment should cover more than software versions. Decision-makers need to understand the shape of risk. For example, a legacy application hosted on ageing infrastructure may be stable, but if deployments are manual, access is shared, logs are local-only and the only knowledgeable engineer has left, the real risk is operational fragility, not just old code. Equally, a newer software stack can still be poorly modernised if reporting is fragmented and sensitive data is copied between tools without governance.
A practical diagnostic checklist includes:
- Application architecture: monolith, modular monolith, services, tightly coupled integrations
- Infrastructure: on-premises, co-location, hybrid, virtual machines, managed platforms, serverless
- Delivery: release frequency, test automation, rollback capability, environment consistency
- Data: source-of-truth systems, duplicated records, batch jobs, schema quality, archival
- Security: identity model, MFA coverage, vulnerability management, logging, backup, disaster recovery posture
- Compliance: privacy obligations, internal controls and sector-specific requirements where relevant
- Cost drivers: licences, hosting waste, support effort, incident frequency, lock-in risk
One of the most important early lessons in many modernization programmes is that product features alone are not enough; role boundaries, data ownership and workflow clarity have to be designed alongside the platform. That is true in most enterprise settings: modernization succeeds when process, permissions and reporting are considered from the start, not bolted on later.
Pick the right modernization path for each system
Not every application deserves the same treatment. The right path depends on value, complexity, risk and time pressure. A finance or operations platform with deep custom rules may be a poor candidate for rapid replacement, while a basic internal portal may be ideal for redevelopment using a modern stack.
A useful way to think about options is by speed versus long-term payoff:
- Rehosting is often fastest when the priority is infrastructure exit, better backup or improved availability. It can reduce operational pain quickly, but it rarely fixes poor architecture, brittle integrations or manual releases.
- Replatforming can be a strong middle ground. Moving to a managed database, supported runtime or standardised deployment platform often improves reliability and supportability without changing business logic too much.
- Refactoring gives greater long-term flexibility, but it needs clearer requirements, stronger engineering discipline and more regression testing. It is usually best for systems that matter strategically and will continue to evolve for years.
- Replacing a system can remove heavy legacy constraints, but migration, user retraining, reporting changes and process redesign are often underestimated.
- Retiring systems is less glamorous than building new ones, yet it is often one of the cleanest ways to reduce cost, attack surface and duplicate work.
There are trade-offs in every route. Rehosting can preserve existing inefficiencies. Refactoring can overrun if teams start redesigning everything at once. Replacing can create business disruption if workflows are not mapped in detail. A good roadmap mixes approaches rather than betting on a single transformation pattern.
As a practical guide, quick-win initiatives often include identity modernisation, central logging, test automation, environment standardisation and API enablement. Higher-effort programmes usually include data model redesign, service decomposition, workflow changes and retirement of entrenched legacy tools.
Build a realistic roadmap, budget and timeline
One reason enterprise modernization loses support is that plans are either too vague or too ambitious. A better approach is to define phases with visible outcomes, realistic dependencies and decision points. That allows leaders to release budget in stages and adjust if priorities change.
A typical roadmap might look like this:
- Discovery and prioritisation: 2 to 6 weeks
- Foundation work: 1 to 3 months
- First modernization wave for one or two priority systems: 3 to 6 months
- Broader rollout across connected systems: 6 to 12 months or more
Foundation work often includes:
- Single sign-on and stronger access controls
- Centralised monitoring and alerting
- Backup and recovery improvements
- Environment standardisation
- CI/CD pipeline setup
- Integration standards and API governance
Budget ranges vary too much by estate size to pretend otherwise, but estimate categories are still useful. Costs usually come from five places:
- Discovery and architecture planning
- Engineering effort for application and integration changes
- Data migration and cleansing
- Security, testing and compliance activities
- Change management, training and parallel running
A focused modernization of one internal application and its deployment model may be measured in weeks to a few months. A business-critical multi-system programme with data migration, reporting changes and operating model updates can easily run for a year or longer. What matters most is not compressing the schedule artificially, but sequencing work so value appears early and major risks are surfaced before commitments become expensive.
A sensible business case should include both direct and indirect outcomes, such as fewer incidents, shorter lead time for change, less manual rework, improved auditability and reduced dependency on scarce legacy skills. Avoid promises of immediate cost savings if the near-term reality is dual-running and migration overhead. In many cases, the first return is reduced risk and faster delivery, with operating savings arriving later.
Data, integration and security are usually the hardest parts
Many modernization plans focus on applications first because screens and workflows are visible. In practice, the harder work is often underneath: inconsistent data, undocumented interfaces and uneven security controls. If these are not addressed early, the programme may deliver a nicer front end while preserving the same bottlenecks.
Data modernization should answer a few uncomfortable questions:
- Which system is the source of truth for each critical entity?
- Where is the same data duplicated, transformed or manually corrected?
- What reporting depends on brittle extracts or spreadsheets?
- Which historical records must be migrated, archived or left in place?
- What data quality rules are needed before automation can be trusted?
Migration strategy matters. A full cutover can simplify the end state, but carries more operational risk. Phased migration reduces disruption, yet introduces temporary complexity because old and new systems need to stay aligned. In either case, reconciliation rules, test cases and ownership should be explicit.
Integration decisions also deserve more rigour than simply choosing APIs everywhere. Some business processes need immediate response and suit synchronous APIs. Others work better as events or queued messages, especially where reliability, retries and decoupling matter. Batch processing is not automatically obsolete either; for some reporting or low-frequency transfers, it remains the simplest option.
Security modernization should not wait until the final release hardening phase. Prioritise controls that reduce systemic risk across the estate:
- Central identity and role-based access
- MFA for privileged and remote access
- Secrets management instead of embedded credentials
- Standard logging with retention and audit trails
- Vulnerability and patch management discipline
- Tested backup and recovery procedures
A common pitfall is adding new integration paths faster than governance can keep up. The result is more hidden dependencies, not less. To avoid that, define naming standards, ownership, versioning rules and decommission dates for interfaces as part of the roadmap.
Common pitfalls that slow enterprise modernization
Most modernization failures are not caused by a single technology choice. They usually come from avoidable planning and execution mistakes.
The most common ones include:
- Starting with a complete rebuild before understanding dependencies
- Treating cloud migration as the same thing as modernization
- Underestimating data cleanup, reconciliation and reporting changes
- Ignoring support model changes after go-live
- Running too many workstreams at once with shared subject-matter experts
- Delaying security, testing and observability until late in the programme
- Failing to retire legacy components, which leaves duplicated cost and complexity
- Measuring progress only by delivery milestones rather than business outcomes
There is also a people risk. If users are accustomed to informal workarounds, a modern platform can feel slower at first because controls are clearer and exceptions need to be handled properly. That is not a reason to avoid improvement, but it does mean training, process redesign and local champions matter.
Another subtle pitfall is over-engineering the target state. Teams sometimes introduce containers, event streaming, service meshes and multiple data platforms before the organisation has the operational maturity to run them well. Enterprise modernization should reduce drag, not replace one kind of complexity with another.
How to measure whether modernization is working
A modernization programme needs success measures that go beyond project completion. Finishing a migration says little if releases are still slow, incidents remain frequent or reporting is still stitched together manually.
Useful measures usually combine business and engineering indicators:
- Lead time for change
- Release frequency and rollback success
- Incident volume and mean time to recover
- Manual processing time removed from core workflows
- Audit findings or control gaps reduced
- User satisfaction for critical internal journeys
- Infrastructure or support effort reduced where relevant
- Number of legacy interfaces or duplicate systems retired
Choose a small baseline set before work starts. If possible, compare the old and new process during a pilot or phased rollout. That helps separate real improvement from assumptions.
For governance, a monthly modernization review is often enough for many organisations. It should focus on decisions, risks, dependency management and measurable outcomes, not just status reporting. If a stream is not producing value or has unknown migration risk, it is better to pause and reshape it than to keep spending because the roadmap said so.
In the end, enterprise modernization is successful when it makes future change easier. Systems become simpler to operate, safer to extend and less dependent on tribal knowledge. That is usually the clearest sign that the programme has moved beyond technology refresh into real operational improvement.
Frequently Asked Questions
What is enterprise modernization in simple terms?
Enterprise modernization is the process of updating legacy systems, data, infrastructure, security and delivery practices so the business can change technology faster, more safely and with less operational friction.
Where should an organization start with enterprise modernization?
Start with a business-led assessment of critical systems, dependencies, data quality, security risks and delivery bottlenecks. Prioritize the areas creating the most risk, delay or manual work, then choose whether to retain, rehost, replatform, refactor, replace or retire each system.
Is cloud migration the same as enterprise modernization?
No. Moving workloads to the cloud can be part of enterprise modernization, but on its own it may not fix brittle integrations, poor data quality, weak security controls or slow release processes.
How long does enterprise modernization usually take?
A focused modernization effort for one application or platform may take a few months. A broader multi-system program involving data migration, integrations and operating model changes often takes 12 months or more.
What are the biggest risks in enterprise modernization?
Common risks include underestimating data migration, rebuilding too much too soon, delaying security and observability, failing to map dependencies, and not retiring legacy components after new systems go live.
Work with Esparks IT Solutions
Planning a project around this? We work with businesses in the United States, Canada and the UAE, as well as the UK and Australia. Explore our Programming services and portfolio, estimate your project cost, or book a free call.