If your company is considering internal tools development in Riyadh, the right approach is to build targeted software that removes manual work, improves visibility, and fits your real operating process rather than forcing teams into generic apps. For most Saudi organizations, the best results come from starting with one high-friction workflow, integrating with existing systems such as ERP, CRM, HR, or finance platforms, and designing for security, bilingual use, and long-term maintainability.
Key takeaways
- Internal tools development in Riyadh is most effective when companies start with one painful workflow, define clear user roles, and integrate with the systems employees already use.
- For most Saudi businesses, internal tools deliver more value than generic SaaS when workflows involve approvals, Arabic and English interfaces, local compliance, or ERP-specific processes.
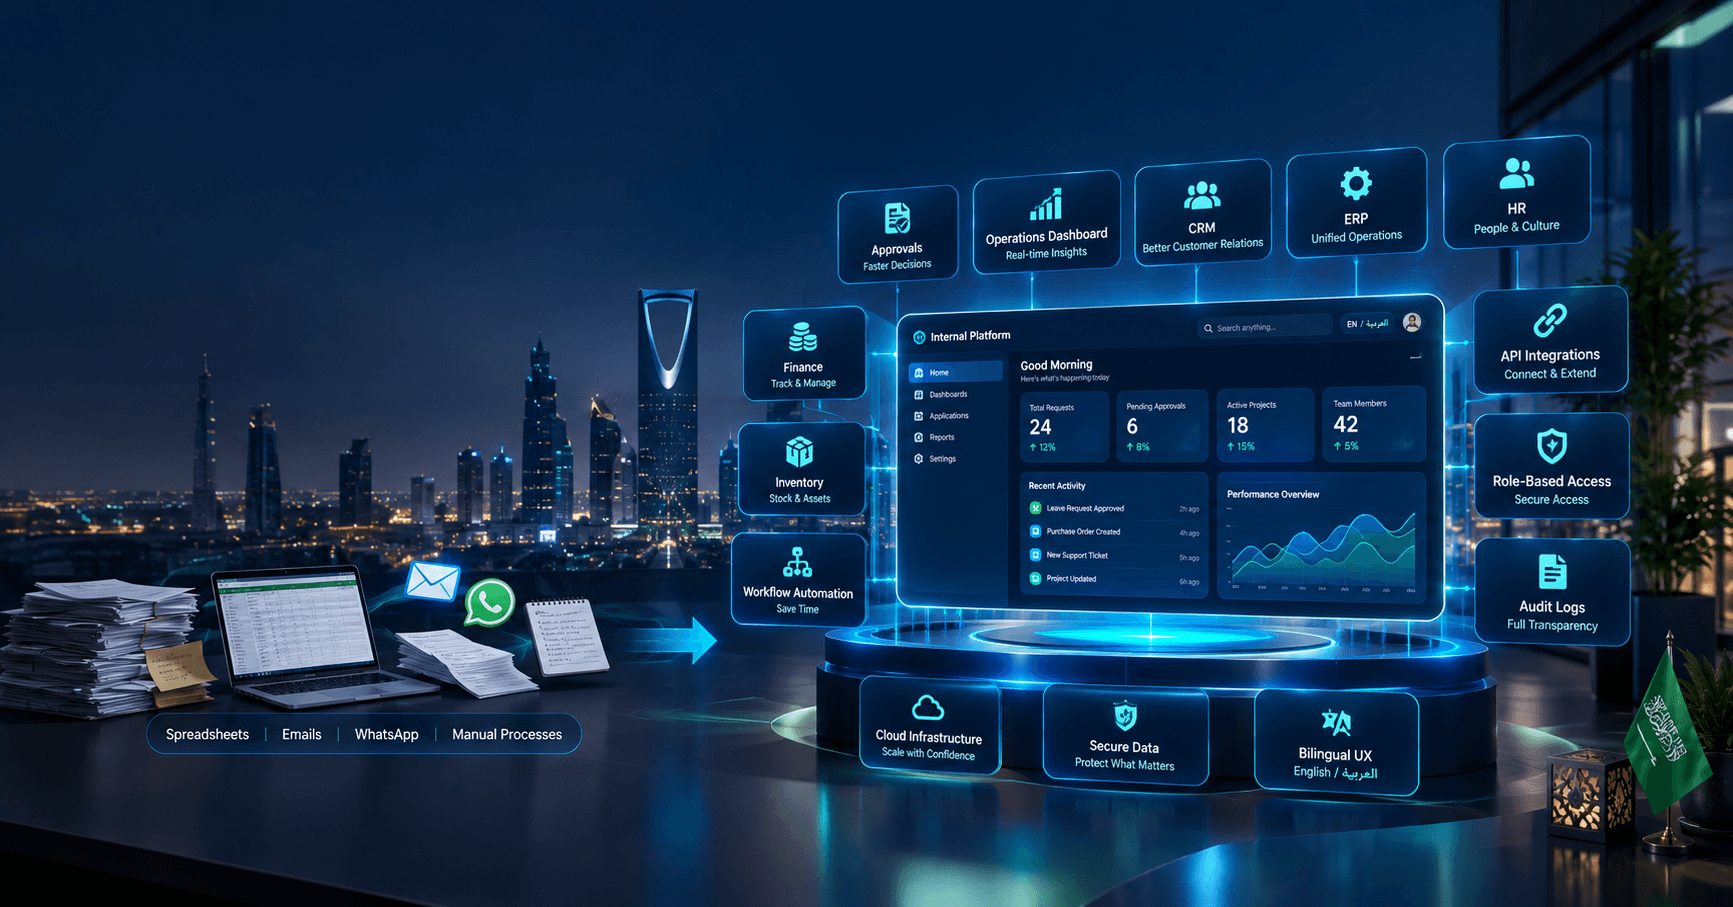
- A reliable internal tool needs role-based access control, audit logs, API-first integration, and deployment standards that fit the organization's cloud, security, and change-management model.
- Typical internal tools can take from a few weeks to several months depending on scope, integrations, and security requirements, so prioritizing a small first release reduces cost and delivery risk.
- The right software partner should be able to explain architecture, data handling, DevOps, and handover clearly, not just design screens or promise fast delivery.
Why businesses build internal tools instead of buying another SaaS product
Internal tools are the software employees use to run the business behind the scenes: approval systems, operations dashboards, CRM extensions, HR workflows, service desks, field-service coordination panels, procurement portals, inventory screens, finance reconciliations, and admin consoles. They are not usually public-facing products, but they often have more direct impact on daily productivity than customer apps because they determine how quickly teams can process requests, approve spending, onboard staff, or act on data.
In Saudi companies, we often see the same trigger: important work is being managed through Excel files, email chains, WhatsApp messages, or disconnected software that cannot reflect the real workflow. A sales manager cannot see delivery status without asking operations. HR onboarding depends on manual checklists. Finance approvals move slowly because there is no clear ownership or audit trail. These are not just inconveniences; they create reporting gaps, duplicated effort, security risk, and decision delays.
Buying off-the-shelf software can be the right choice when the process is standard and the fit is strong. But custom internal tools make more sense when your process is shaped by local approval structures, Arabic and English users, specialized ERP rules, field operations, or unique combinations of departments. The goal is not to custom-build everything. The goal is to custom-build only where process fit creates measurable operational value.
Internal tools development in Riyadh: what good looks like
Good internal tools development in Riyadh starts with process clarity, not code. Before selecting a framework or cloud provider, define the workflow in plain language: who starts the task, what data is required, who approves it, what exceptions exist, what system is the source of truth, and what records must be retained. If a business cannot explain that flow, software will only digitize confusion.
A strong internal tool usually has a few characteristics in common:
- Clear user roles such as requester, approver, operator, manager, and auditor
- Role-based access control with least-privilege permissions
- Integration with existing systems through APIs, webhooks, or secure file exchange
- Searchable records, status tracking, and audit logs
- Mobile-friendly screens for managers and field teams
- Arabic and English support where needed
- Reporting that reflects operational decisions, not vanity metrics
- Deployment and backup practices aligned with security policy
For example, a procurement tool for a Riyadh enterprise might need purchase request creation, multi-level approvals based on spend thresholds, vendor lookup from ERP, attachment support for quotations, finance validation, and an audit trail for every status change. A generic task app might cover 20% of that well. The remaining 80% is where process-specific software becomes valuable.
Choosing the right architecture, stack, and integration model
The best stack depends on your environment, team skills, security requirements, and future roadmap. For many business applications, modern web apps are a practical first choice because they reduce deployment friction and work across desktop and mobile browsers. Typical front-end choices include React, Next.js, Angular, or Vue. On the backend, teams commonly use Node.js with NestJS or Express, Python with Django or FastAPI, .NET, Java Spring Boot, or Laravel for certain business systems.
Database selection should follow data patterns, not hype. PostgreSQL is a solid default for transactional systems because it handles structured relational data well and supports robust indexing, constraints, and reporting queries. MySQL can also work well for many line-of-business apps. Redis is useful for caching and queues. If the tool needs analytics or event processing, you may add services such as Kafka, RabbitMQ, or a warehouse layer later, but many internal tools do not need that complexity on day one.
Integration is usually where projects succeed or fail. Businesses in Saudi Arabia often need tools to connect with Microsoft 365, Azure AD or Entra ID, Google Workspace, SAP, Oracle, Odoo, Salesforce, HubSpot, Zoho, custom ERP modules, payroll systems, or document stores such as SharePoint and S3-compatible object storage. A pragmatic approach is to make the tool API-first, use secure token-based authentication, map source-of-truth ownership early, and handle retries, failures, and duplicate records explicitly. In our experience, many delays come not from building the screens but from unclear ownership of master data and edge cases in integration.
Cloud and deployment choices should also be deliberate. AWS, Azure, and Google Cloud all support strong enterprise deployments. A typical setup may include containerized services using Docker, orchestration with Kubernetes where scale justifies it, CI/CD pipelines through GitHub Actions, GitLab CI, or Azure DevOps, centralized logging with ELK or managed observability tools, secrets management, and infrastructure as code using Terraform. Smaller tools may not need full Kubernetes from the start; a managed app service or container platform is often enough.
A step-by-step framework to scope the right internal tool
Many internal projects become expensive because the first scope is too broad. A better method is to define a narrow first release that solves one painful workflow end to end. This lets the business validate adoption, data quality, and exception handling before investing in advanced reporting or automation.
A practical decision framework looks like this:
-
Identify the bottleneck. Choose a process where delays, rework, or lack of visibility are frequent. Good candidates include approvals, service requests, dispatching, onboarding, compliance checklists, asset tracking, and cross-team handoffs.
-
Map the workflow in detail. Document users, steps, inputs, outputs, exceptions, and dependencies. Include who currently owns each part and where data lives today.
-
Define the source of truth. Decide which system owns customer, employee, vendor, inventory, or finance data. This avoids the common mistake of creating conflicting records in multiple systems.
-
Prioritize the minimum useful release. Separate must-have features from nice-to-have requests. A first release often needs forms, statuses, approvals, notifications, and reporting; it rarely needs every automation the business can imagine.
-
Choose the integration pattern. Decide whether to use direct APIs, scheduled sync, event-driven updates, or secure imports. This affects complexity, reliability, and timeline.
-
Design for governance. Include permissions, audit trails, retention rules, and admin controls from the start. Retrofitting governance later is usually expensive.
-
Plan rollout and ownership. Decide who will support the tool, handle user access, approve changes, and monitor adoption after launch.
A useful scoping rule is to ask, “What can be shipped in the first version that still removes meaningful manual work?” If you cannot answer that clearly, the project is still too vague. When we built GitHub Timesheet, the value came not from adding every possible feature but from structuring the workflow around a specific operational need and ensuring the system reflected how people actually worked.
Security, compliance, and governance for Saudi organizations
Security matters more in internal tools than many teams expect because these systems often touch employee records, financial approvals, customer data, or operational controls. At minimum, the application should support secure authentication, role-based access control, encrypted data in transit with TLS, encrypted storage where appropriate, audit logging, session management, and backup and recovery procedures. If the tool will be used by admins or finance teams, add stronger controls such as IP restrictions, MFA enforcement, and privileged-action logging.
Identity and access management should be integrated with the organization's existing directory where possible. SSO through SAML or OpenID Connect simplifies onboarding and offboarding while reducing password risk. For larger enterprises, access should follow group-based provisioning rather than manual user-by-user configuration. That is more maintainable and easier to audit.
Governance also includes data lifecycle decisions. How long should approval records be retained? Who can export data? Which actions need dual approval? What happens if an employee leaves the company? These questions should be resolved during design, not after launch. For organizations in regulated sectors or with strict internal audit requirements, documenting controls is as important as implementing them.
It is also wise to establish coding and deployment standards early: peer review, branch protection, secret scanning, dependency updates, vulnerability scanning, and environment separation across development, staging, and production. A lightweight but disciplined DevSecOps approach usually prevents the most common issues without slowing teams down unnecessarily.
Typical timelines, cost ranges, and what actually drives them
Decision-makers usually ask two practical questions: how long will it take, and what will it cost? The honest answer is that internal tools vary widely because the main cost drivers are scope, number of user roles, integrations, compliance requirements, and change management. A small workflow tool with basic forms, approvals, and reporting can often be delivered in a few weeks to a couple of months. A multi-department platform with ERP integration, SSO, custom dashboards, and strict audit needs may take several months or more.
Typical budgets also vary by architecture and delivery model. A focused MVP for a single workflow may fit a modest budget if the process is clear and integrations are limited. Costs rise when there are multiple external systems, legacy dependencies, bilingual UX, complex permissions, mobile use cases, or heavy reporting. Infrastructure, support, and future enhancement planning should be considered alongside build cost; a cheap first release can become expensive if it is difficult to maintain.
What actually controls time and budget is not just code volume. These factors matter more than many buyers expect:
- Quality and availability of business stakeholders for discovery
- Clarity of workflow exceptions and approval rules
- API readiness of existing systems
- Data cleanup needed before migration or sync
- Number of departments involved in sign-off
- Security review and procurement processes
- Whether the first release is tightly prioritized
A sensible way to reduce risk is phased delivery. Start with discovery and technical design, then build the smallest production-ready version, then add automation, analytics, and broader integrations in later phases. This approach helps leadership assess value earlier and avoids paying for features employees may not use.
Common pitfalls when hiring a partner or running the project internally
One common mistake is treating internal tools as “simple admin software” that can be rushed without product thinking. Internal users may not be external customers, but adoption still depends on usability, performance, clear permissions, and trust in the data. If the tool is confusing or unreliable, employees will revert to spreadsheets and side channels.
Another frequent problem is over-customization too early. Teams try to encode every exception from day one, which produces a large scope, hard testing cycles, and slow releases. It is usually better to standardize 70-80% of the process first and handle rare edge cases manually until patterns become clear. This keeps the first release manageable.
When evaluating a software partner, look beyond visual design and headline pricing. The stronger questions are:
- Can they map business workflows before proposing features?
- Can they explain trade-offs between custom build and SaaS extension?
- Do they have a clear integration approach for ERP, CRM, identity, and document systems?
- How do they handle RBAC, audit logs, backup, observability, and incident response?
- Will they provide architecture documentation, code standards, and handover materials?
- Can they support iterative releases instead of insisting on a rigid big-bang launch?
A credible partner should also be comfortable discussing test strategy. For internal tools, that often means unit tests for business logic, integration tests for APIs, end-to-end tests for critical workflows, and user acceptance testing with real process owners. This is especially important when approvals, financial controls, or HR actions are involved.
The most successful projects usually have a business champion, an IT owner, and a small working group of actual users. That combination keeps the tool aligned with real operations while ensuring technical governance is not an afterthought. At Esparks, we have seen that internal tools create the most value when they are treated as operational infrastructure: purpose-built, well-integrated, secure, and designed to evolve with the business rather than patch over process issues.
Frequently Asked Questions
What is internal tools development in Riyadh?
Internal tools development in Riyadh refers to building custom software used by employees inside a company to manage operations, approvals, reporting, service workflows, or administrative tasks. These tools are designed around the organization's actual process, integrations, security rules, and language needs rather than public customer use.
When should a Saudi business choose a custom internal tool instead of SaaS?
A Saudi business should consider a custom internal tool when the workflow depends on unique approval logic, ERP-specific data, bilingual interfaces, local governance requirements, or several systems that do not work well together out of the box. If the process is standard and a SaaS product fits well with minimal customization, buying may be the better option.
How long does an internal tool project usually take?
A small internal tool with a clear workflow and limited integrations can often be delivered in a few weeks to a couple of months. More complex systems involving SSO, ERP integrations, strict permissions, custom dashboards, and multiple departments typically take several months because discovery, testing, and governance add meaningful effort.
What security features should an internal tool include?
At a minimum, an internal tool should include secure authentication, role-based access control, encrypted connections, audit logs, backup procedures, and proper environment separation between development and production. For finance, HR, or admin use cases, it is also advisable to add SSO, MFA, privileged-action logging, and clear data retention and export controls.
Work with Esparks IT Solutions
Planning a project around this? We work with businesses in the United States, Canada and the UAE, as well as the UK and Australia. See a related project: GitHub Timesheet. Explore our Programming services and portfolio, estimate your project cost, or book a free call.