If you are looking for a Software Development Company in Stoke-on-Trent, choose a partner that can translate business goals into a clear delivery plan, not just a stack of technologies. The right team should show how they will discover requirements, reduce delivery risk, design secure architecture, and support the software after launch.
Key takeaways
- A strong software partner should clarify business outcomes, technical constraints, delivery risks and support responsibilities before writing code.
- For most business systems, the quality of discovery, architecture and DevOps matters as much as the hourly rate because weak foundations are expensive to fix later.
- Typical custom software projects vary widely, but many SME builds take roughly 8-24 weeks for an initial release, with larger platforms running longer in phased increments.
- Security, data protection, access control, backups, monitoring and incident response should be designed into the project from the start, not added after launch.
- The best way to compare software suppliers is to score them against the same brief, team model, delivery method, communication plan and post-launch support terms.
For founders, CTOs and IT managers, the real question is rarely who can code. It is who can build the right thing, in the right order, with realistic costs, governance and operational resilience. That is the difference between a useful business system and an expensive rebuild.
What a strong software partner should actually do
Many buyers start by comparing rates, portfolios and promises. In practice, those are weak signals on their own. A reliable software partner should help you define the problem, challenge vague assumptions, and turn a broad idea into a sequence of deliverable outcomes.
At a minimum, a business-focused software team should be able to cover:
- Discovery: stakeholder interviews, process mapping, user journeys, requirements prioritisation and technical risk review
- Product definition: scope, acceptance criteria, release planning, backlog management and success measures
- Solution design: architecture, database model, API strategy, integration approach and non-functional requirements
- Delivery: coding standards, version control, peer review, automated testing and deployment pipelines
- Operations: hosting, monitoring, logging, alerting, backup policy and support ownership
- Security and compliance: access control, encryption, audit trails, GDPR considerations and incident handling
This matters because software is rarely a single deliverable. A customer portal may need identity management with Microsoft Entra ID or Auth0, payment integration with Stripe, CRM sync with HubSpot or Salesforce, cloud hosting on Azure or AWS, reporting through Power BI, and mobile access via React Native or Flutter. A good partner connects these moving parts into one maintainable system instead of shipping a bundle of loosely joined tools.
How to evaluate a Software Development Company in Stoke-on-Trent
When assessing a Software Development Company in Stoke-on-Trent, ask how they make decisions under uncertainty. Most projects begin with incomplete information: changing workflows, legacy systems, inconsistent data, or internal disagreement about priorities. A mature team will have a process for handling that uncertainty without letting scope drift out of control.
A practical way to compare suppliers is to use the same decision framework for each one:
- Define the business problem in plain language. For example: reduce manual order entry, replace spreadsheet-based approvals, or unify customer data across sales and service.
- List the non-negotiables. These might include UK GDPR alignment, integration with Sage, Microsoft 365, SAP or Xero, SSO, audit logs, or role-based access.
- Ask for a proposed delivery approach. You want to hear how discovery will run, what will be documented, which assumptions must be tested first, and how changes will be handled.
- Review the team composition. A credible proposal usually includes some mix of product lead, solution architect, UX designer, developers, QA and DevOps support rather than only developers.
- Examine examples of similar complexity. Similarity is not about industry labels alone; it is about workflows, integrations, compliance needs and scale.
- Clarify post-launch ownership. Confirm support hours, SLA structure, bug triage, patching, cloud costs, and whether knowledge transfer is included.
The strongest conversations are usually specific. Instead of asking, "Can you build a custom platform?" ask, "How would you phase a multi-tenant SaaS product with a client admin portal, billing, notification workflows and Power BI reporting?" Specific questions quickly reveal whether a supplier thinks in business systems or generic development templates.
Delivery models, architecture and technology choices
Business buyers do not need to choose every framework themselves, but they should understand the consequences. The wrong architecture can make a product expensive to change; the wrong delivery model can create friction between your internal team and the supplier.
For modern business applications, common choices include:
- Web applications: React, Angular or Vue on the front end; .NET, Node.js, Java, Python Django or Laravel on the back end
- Mobile apps: Flutter or React Native for cross-platform delivery; Swift and Kotlin for fully native builds when device-specific performance matters
- APIs and integrations: REST or GraphQL, webhooks, OAuth 2.0, OpenID Connect and middleware for ERP, CRM or payment systems
- Data platforms: PostgreSQL, SQL Server, MySQL, MongoDB, Redis, Elasticsearch and managed data services in Azure, AWS or Google Cloud
- Cloud and DevOps: Docker, Kubernetes where justified, GitHub Actions, GitLab CI/CD, Azure DevOps, Terraform and Infrastructure as Code
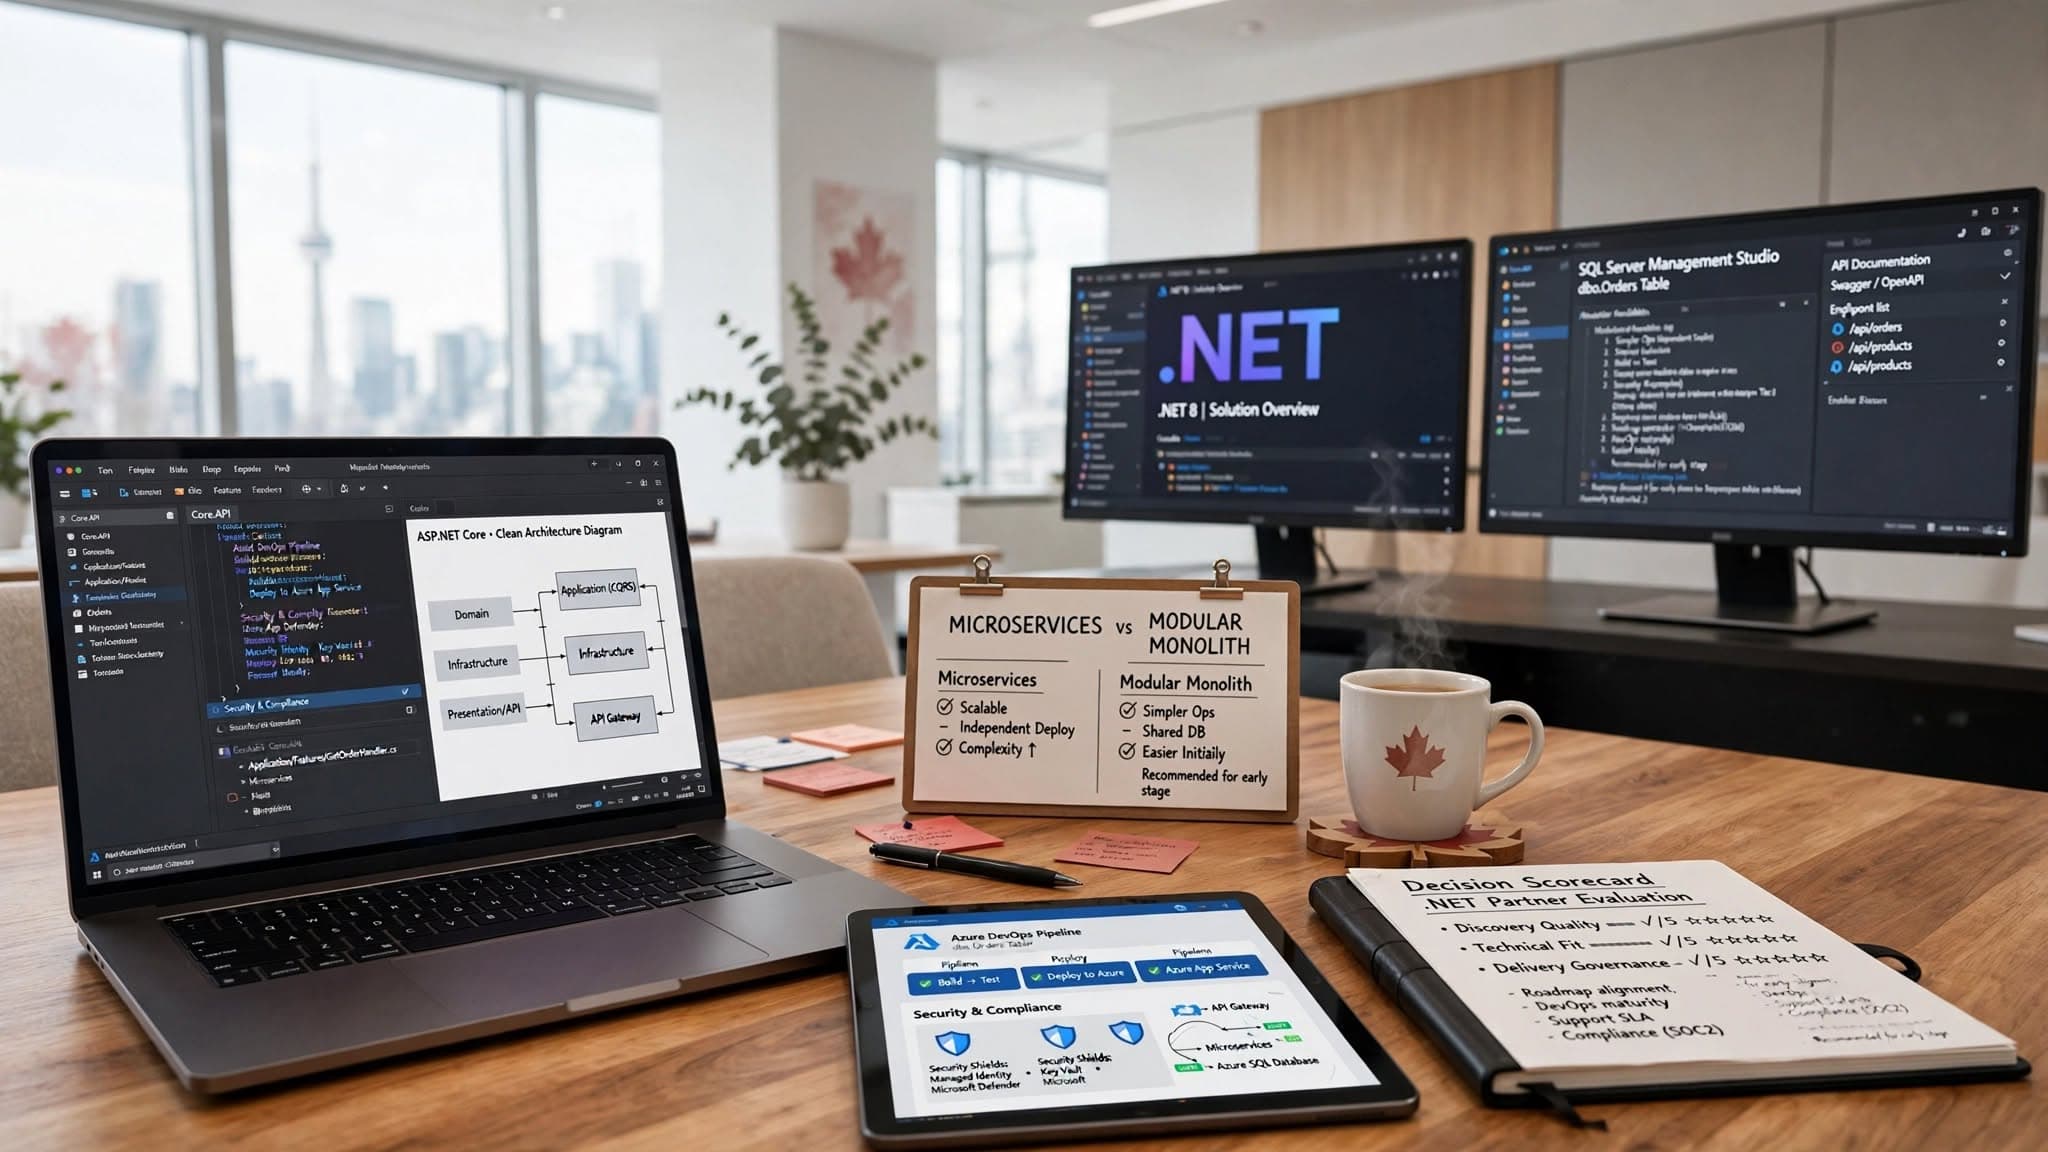
A common mistake is overengineering early. Not every system needs microservices, Kubernetes or event-driven architecture on day one. For many SMEs, a modular monolith with clean APIs, strong test coverage and automated deployment is faster to deliver and simpler to maintain. Microservices become more useful when you have multiple teams, independent scaling needs, or clear service boundaries such as billing, messaging and analytics.
Another point to test is technical decision-making around integrations and extensibility. Suppose you run a manufacturing or distribution business and need stock, pricing and fulfilment data from an ERP while giving customers a self-service portal. The software should be designed so that future integrations, such as EDI, warehouse scanning or customer-specific pricing rules, do not require a major rewrite. That usually means disciplined domain modelling, documented APIs, consistent event handling and clear separation between core business logic and external systems.
Security, compliance and operational readiness
For UK organisations, security is not a premium add-on. It is a baseline requirement. Even if your project is not in a highly regulated sector, the software should still address identity, permissions, data retention, auditability, resilience and patching from the start.
At a practical level, ask how the team handles:
- Authentication and authorisation, including SSO, MFA and role-based access control
- Encryption in transit with TLS and encryption at rest where appropriate
- Secret management using secure vaults rather than configuration files
- Logging and monitoring through tools such as Azure Monitor, Application Insights, Datadog, Grafana or ELK
- Backup, restore testing and disaster recovery planning
- Dependency and container scanning, patch management and vulnerability remediation
- Secure development practices aligned with OWASP guidance
Compliance should also be discussed in business terms. If personal data is involved, data flows, lawful basis, retention rules and processor responsibilities must be understood. If your teams work with NHS-adjacent workloads, finance data or sensitive employee information, you may also need stronger audit controls, environment separation and stricter supplier due diligence. In our experience at Esparks, many project issues that appear technical are really governance gaps: unclear data ownership, no environment policy, weak access reviews or missing support responsibilities.
Operational readiness is the final test before launch. A release is not complete when the code works in staging. It is complete when backups are configured, alerts are meaningful, deployment rollback is tested, support contacts are known, and someone owns routine maintenance. That is how businesses avoid the all-too-common situation where software goes live successfully but becomes fragile within months.
Typical costs, timelines and scoping trade-offs
Custom software pricing varies because complexity varies. A client portal with login, forms, dashboards and a couple of integrations is very different from a workflow platform with mobile access, third-party APIs, approval chains, reporting, document handling and multi-site user roles.
As a broad guide, many projects fall into these typical ranges:
- Discovery and solution design: often 1-3 weeks for a focused SME project, longer for enterprise environments with multiple stakeholders and legacy systems
- MVP or first production release: often around 8-16 weeks for a well-bounded web platform or internal operations tool
- Larger custom platforms: often 4-9 months or more depending on integrations, compliance, migration and team size
- Ongoing support and roadmap delivery: usually structured as retained capacity, ticket-based support, or a blended model
The biggest cost drivers are usually not lines of code. They are integration complexity, unclear requirements, migration from legacy data, edge-case business rules, environment setup, and security or audit needs. For example, building a simple field service mobile app is one level of effort; syncing offline data, generating job sheets, attaching photos, integrating with scheduling software and enforcing supervisor approvals is another.
A sensible supplier should help you reduce cost by reducing uncertainty. Typical methods include phased releases, prototype-first validation, narrowing the initial user group, deferring non-essential features, and using proven cloud services rather than building everything from scratch. If a proposal gives a highly precise figure before discovery, treat that as a warning sign rather than reassurance.
Common pitfalls and how to avoid them
Most software failures are avoidable. They usually happen because decisions were rushed, responsibilities were fuzzy, or business rules were never made explicit.
The most common pitfalls we see include:
- Starting with features instead of outcomes. If you cannot state the operational problem clearly, the backlog will sprawl.
- Treating discovery as overhead. Skipping workshops and process mapping often leads to avoidable rework.
- Ignoring internal ownership. A supplier can build the system, but someone on your side must own decisions, feedback and rollout.
- Underestimating data work. Cleansing, mapping and migrating data often take longer than expected.
- Weak acceptance criteria. "Build a dashboard" is not a testable requirement; define users, data sources, permissions and actions.
- No post-launch plan. Without monitoring, patching and support workflows, even good software becomes brittle.
To avoid these traps, use a simple governance structure. Appoint one business owner, one technical owner and one approval route for scope changes. Ask for a living backlog, fortnightly demos, risk logs and release notes. Require environments for development, testing and production. Confirm where source code is stored, who owns repositories, and how handover will work if the relationship changes.
Also pay attention to user adoption. Even a technically solid system can fail if it disrupts established workflows without training, staged rollout or feedback loops. For example, replacing a spreadsheet process with a web portal may improve control, but if the portal adds too many mandatory steps too early, frontline teams may route around it. Good implementation balances control with usability.
A practical shortlist and selection process
If you are narrowing suppliers, keep the process lightweight but disciplined. A good procurement approach does not need to be bureaucratic; it just needs to make suppliers answer the same real-world questions.
A practical shortlist process looks like this:
- Prepare a concise brief covering business problem, target users, current systems, must-have integrations, security needs and preferred timeline
- Ask each supplier for a proposed discovery plan, team structure, assumptions, major risks and support model
- Run a technical and commercial review meeting with the same agenda for each supplier
- Score responses against weighted criteria such as domain understanding, delivery approach, architecture thinking, communication quality, risk management and post-launch support
- Request visibility into working practices such as sprint demos, QA process, repository management and release governance
The goal is not to find the supplier with the flashiest deck. It is to find the one most likely to deliver predictably, communicate clearly and make sound trade-offs when plans change. For businesses in Stoke-on-Trent and across the wider UK, locality can help with workshops and stakeholder alignment, but delivery maturity matters more than postcode alone.
A capable software partner should leave you with more clarity after the first few conversations, not less. If the scope is sharper, the risks are more visible, the architecture choices are easier to understand and the path to an initial release is concrete, you are probably talking to the right kind of team.
Frequently Asked Questions
What should I look for in a Software Development Company in Stoke-on-Trent?
Look for a company that can explain its discovery process, architecture approach, security practices, testing standards and post-launch support model in clear business terms. The best suppliers connect software decisions to operational outcomes, integrations, compliance needs and total cost of ownership.
How long does a custom software project usually take?
A focused discovery phase often takes 1-3 weeks, while a first release for a well-defined web or internal business application commonly takes around 8-16 weeks. More complex platforms with several integrations, mobile apps, legacy migration or stricter compliance requirements usually take longer and are best delivered in phases.
Is it better to choose a local UK software company or a remote team?
A local UK partner can help with workshops, stakeholder communication, shared business context and alignment with UK data protection expectations. However, delivery discipline, technical quality, documentation, DevOps maturity and support ownership are usually more important than physical location alone.
How can I compare software suppliers fairly?
Give each supplier the same written brief and ask for the same outputs: discovery plan, team structure, architecture assumptions, delivery method, risk register and support terms. Comparing against a consistent scorecard is more reliable than judging polished presentations or hourly rates in isolation.
Work with Esparks IT Solutions
Planning a project around this? We work with businesses in the United States, Canada and the UAE, as well as the UK and Australia. See how we work with clients in the UK. Explore our Programming services and portfolio, estimate your project cost, or book a free call.